3 min read
thucde.dev isn’t just more polished: it has a cleaner frontend, stronger editor, better security, and a more reliable deploy flow.
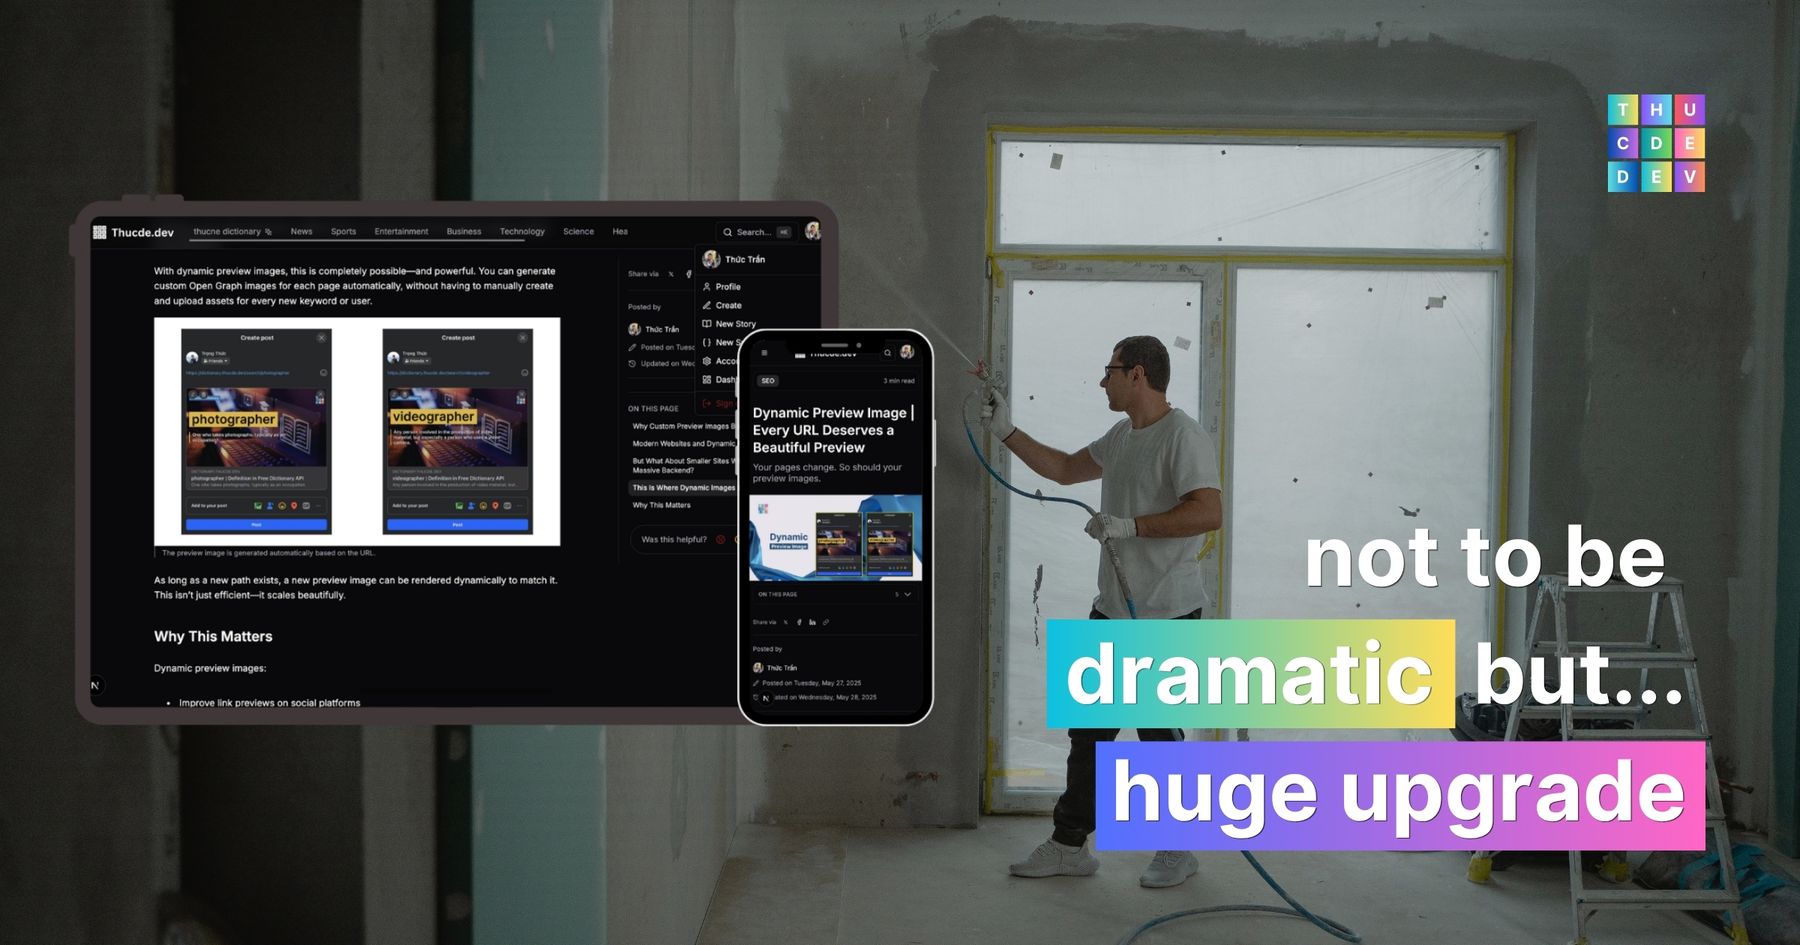
If you only glance at the homepage or a couple of dashboard screens, the easy reaction is probably: “Looks like some nice UI polish.”
One of the biggest shifts is that the frontend no longer feels like a codebase living between two eras.
Over just a few days, thucde.dev
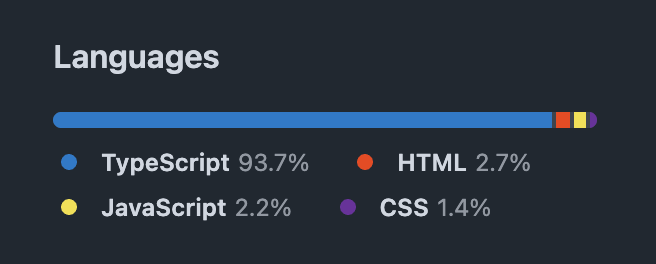
On paper, that can sound like a pile of technical debt work. But that is also exactly why it matters.
Small products often get stuck in a half-old, half-new state for a long time: newer components on top, older state assumptions underneath; App Router in place, but still a client-heavy mental model; TypeScript installed, but not strict enough to catch the bugs that matter early. The result is that every change carries extra fear.
What changed here is not just the UI layer. It is the combination of three deeper improvements happening together:
Most readers will not notice that directly, and that is fine. Maintainers will. This is the kind of change that makes the next feature cheaper, safer, and faster to ship.
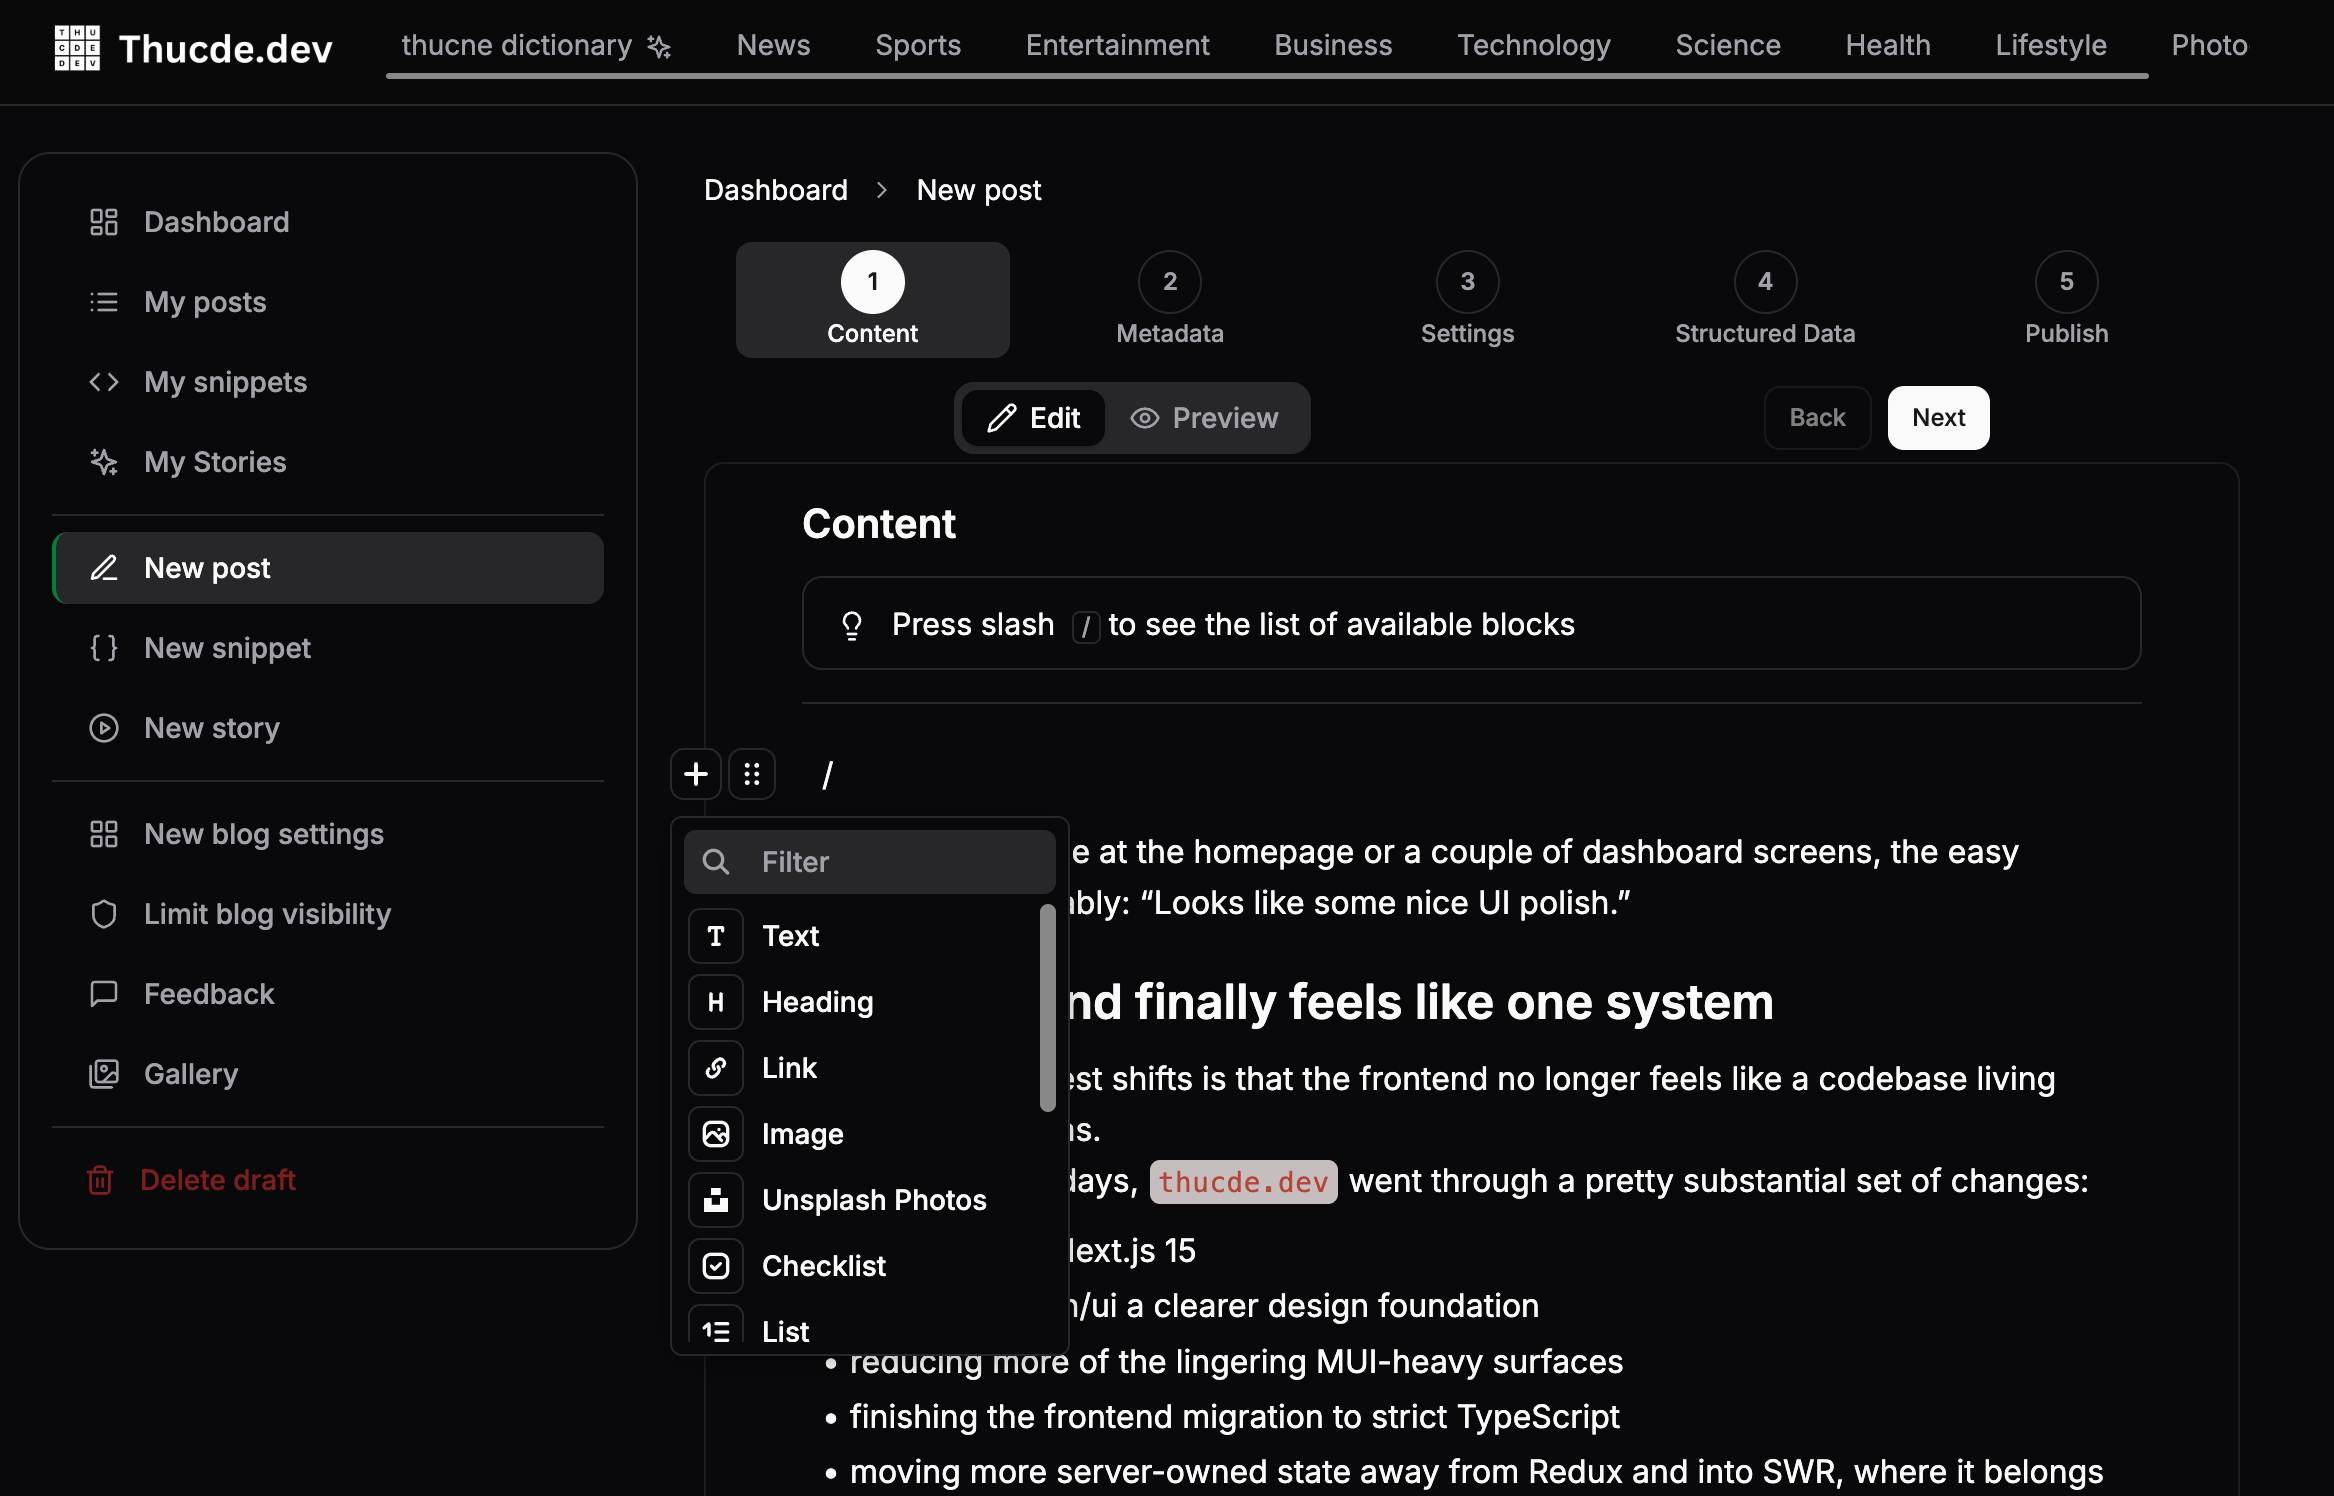
If I had to pick the most visible improvement to show off, it would probably be the authoring experience.
The editor got a serious amount of attention in this "sprint":
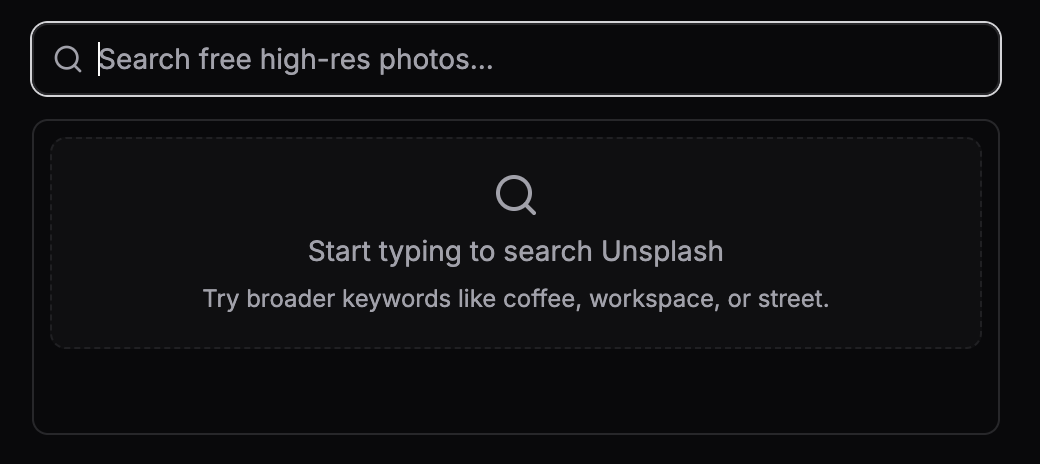
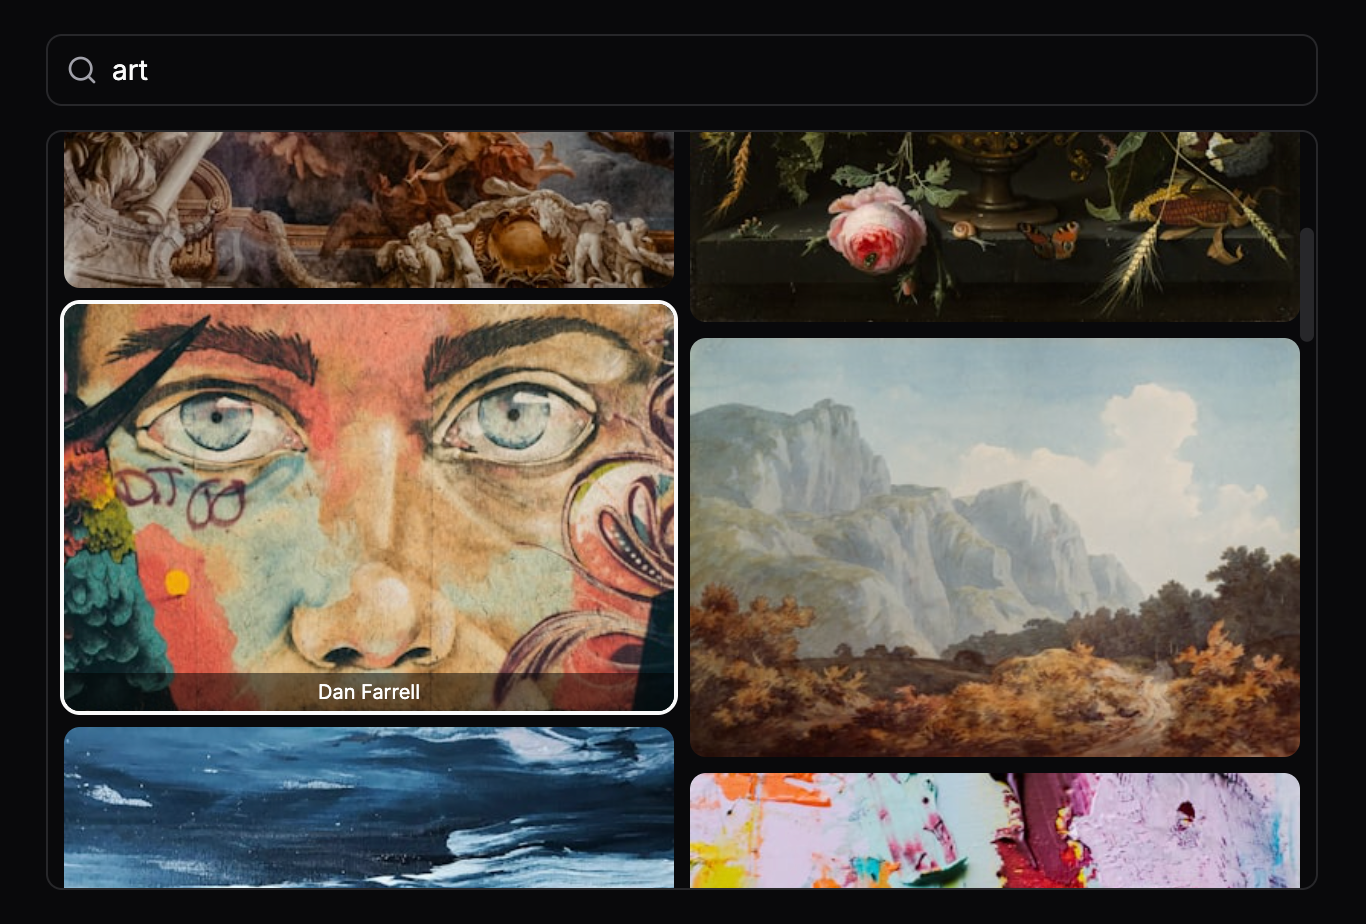
And the image is automatically added with a proper attribution!
With the Embed plugin, Thuc can drop in posts and media from most major social platforms with almost no friction.
And more..!
What I like about this set of changes is that it does not only answer “what can the editor do now?”
It also answers the more important question: “is writing and publishing more trustworthy now?”
For a site like thucde.dev
Another part of this sprint that feels especially worth mentioning, even if it is not flashy, is the security work.
Across both the backend and frontend, there were a number of meaningful improvements:
Why does this matter so much?
Because on a content platform, the dangerous edges often hide in exactly the places that feel the most convenient: rendering HTML, accepting external URLs, exposing metadata for private content, or leaving behind a few helpful local/dev routes.
Problems like that do not always explode immediately. More often, they slowly turn into the kind of platform you stop trusting to extend confidently. So in this case, security is not just hygiene. It is part of what makes future progress possible.
For example:
None of that makes for a dramatic screenshot. But if you are the person running the site, this is exactly the layer that turns a system from “it works” into “it holds up.”
When builds stop trying to do too much at once, deploys get less fragile.
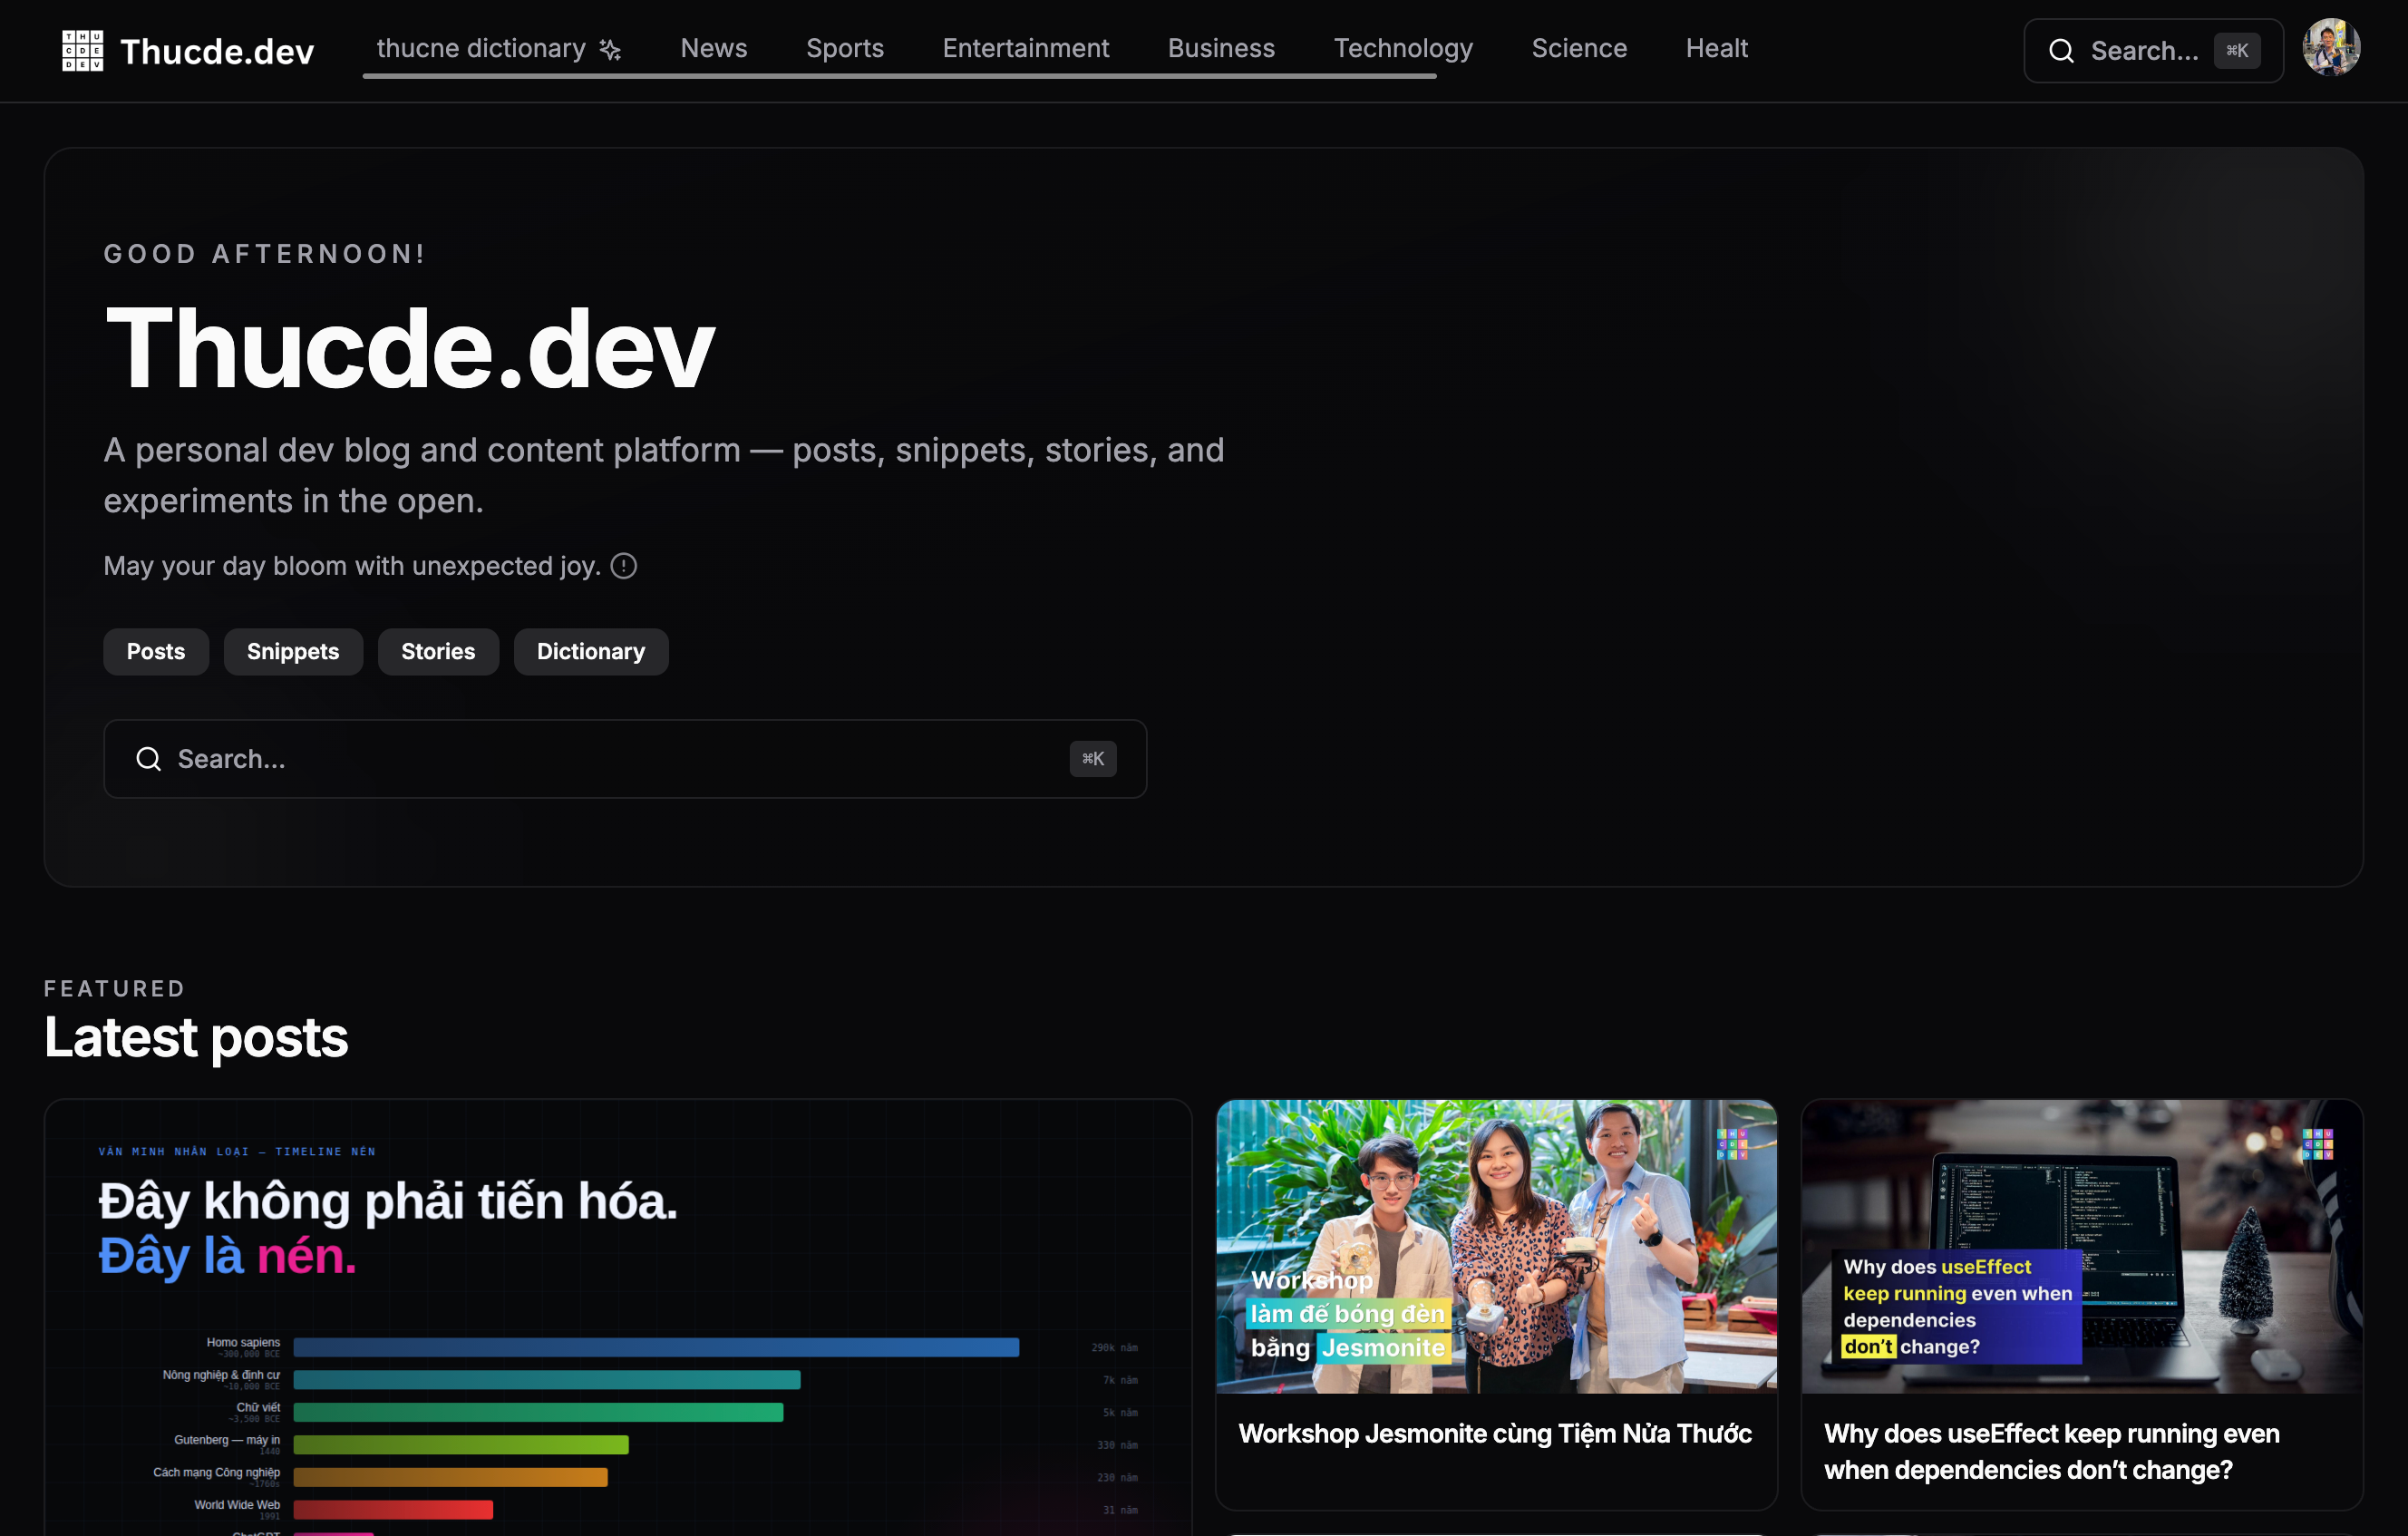
thucde.dev
Thanks for reading!